Fix your weaknesses before AI finds them
We scan your systems all the time, fix what we find, and keep you up to date in Slack and in your dashboard.
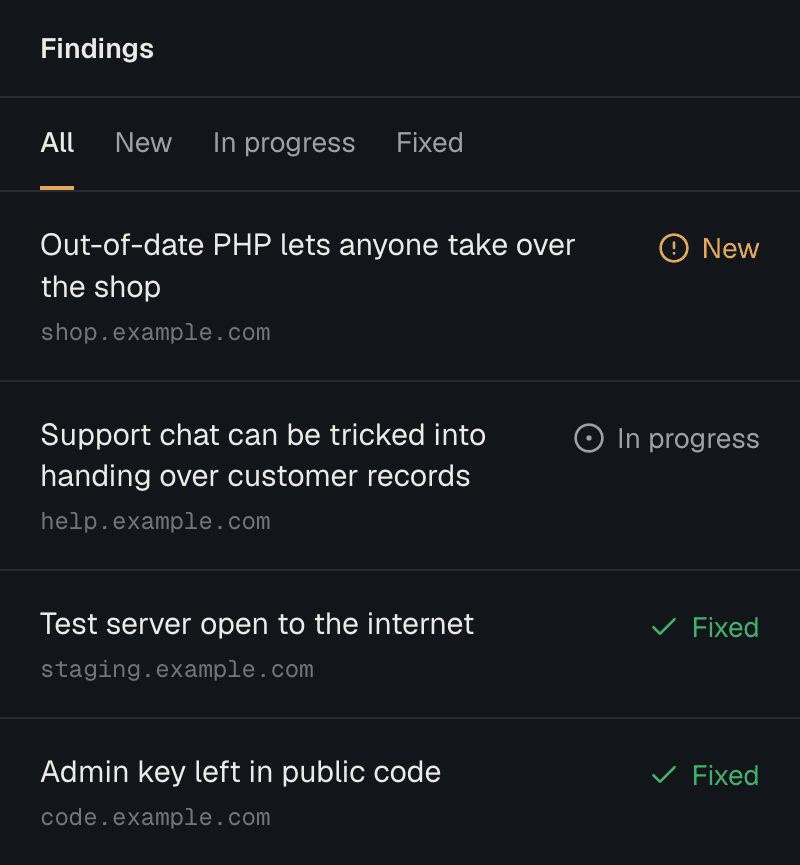
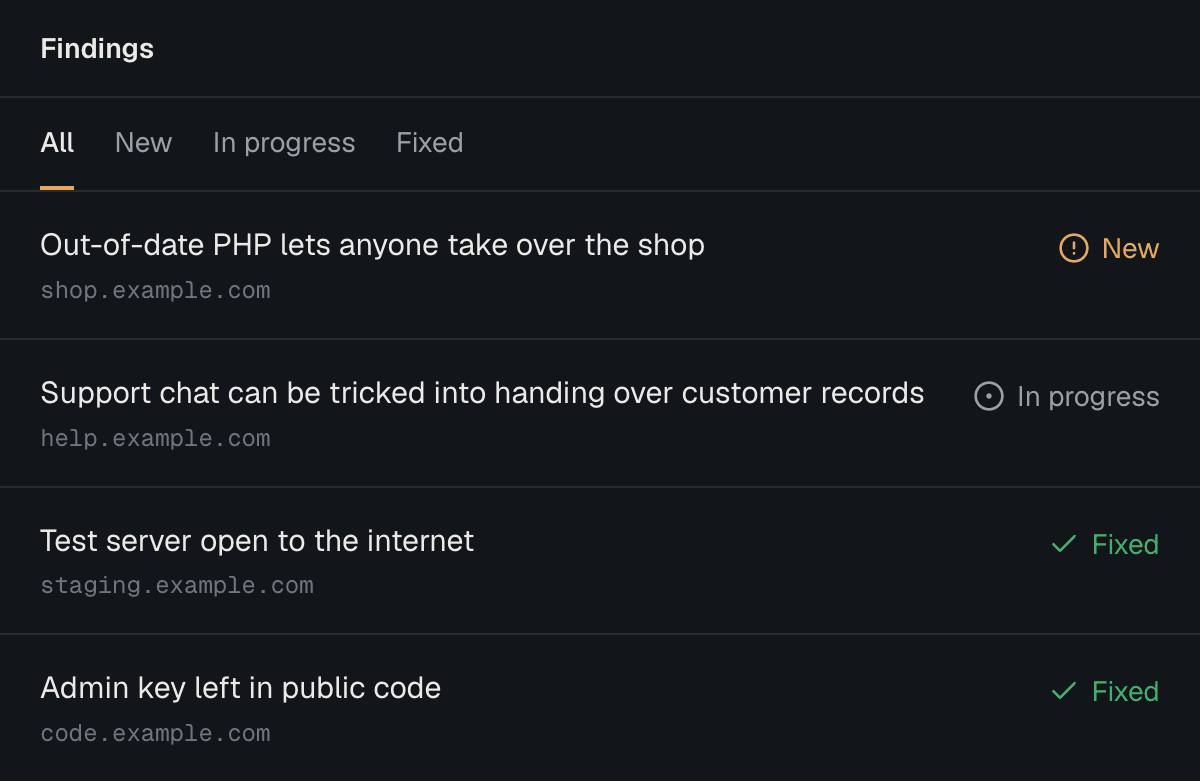
Attackers can now use AI to look for your weak points
Someone can point an AI model at your systems and have it search for mistakes around the clock. In November, Google’s security researchers reported attackers running AI tools that find and exploit software flaws with no person directing each step. AI also makes it faster to turn a published security update into an attack, which leaves less time to apply it. We find the gaps first and fix them for you.
How Kaspian works
Scan
We scan your infrastructure all the time, so a mistake made this week does not sit unnoticed until next year’s test.
Catalog check
Every scan is checked against a catalog of weaknesses that we keep up to date. It is built from open-source red-teaming communities, the people who test systems by attacking them.
Patch
We do the patching too. When a scan finds a weakness, we fix it, so the work does not land on your team.
Weekly human update
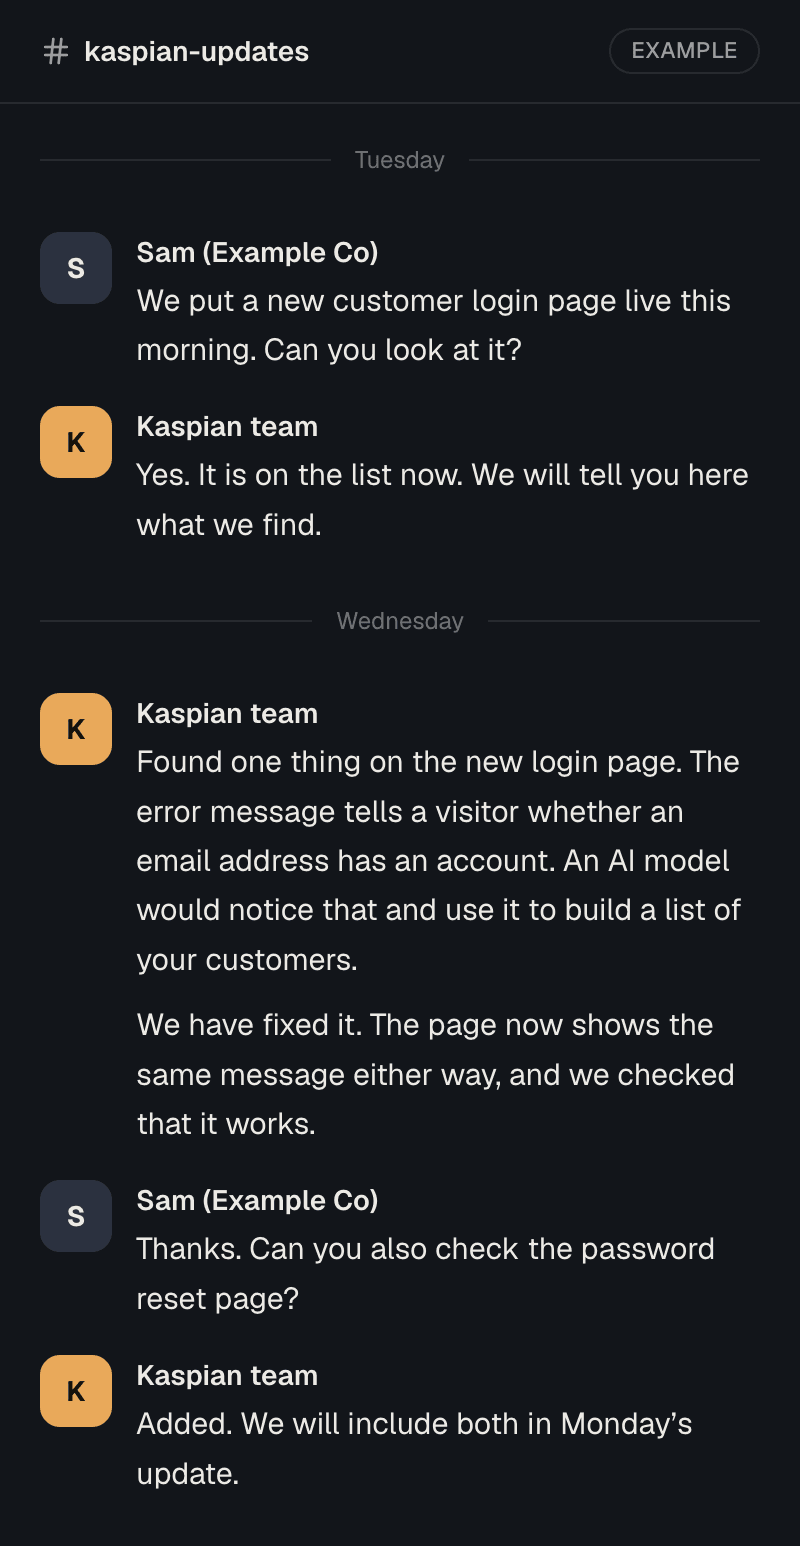
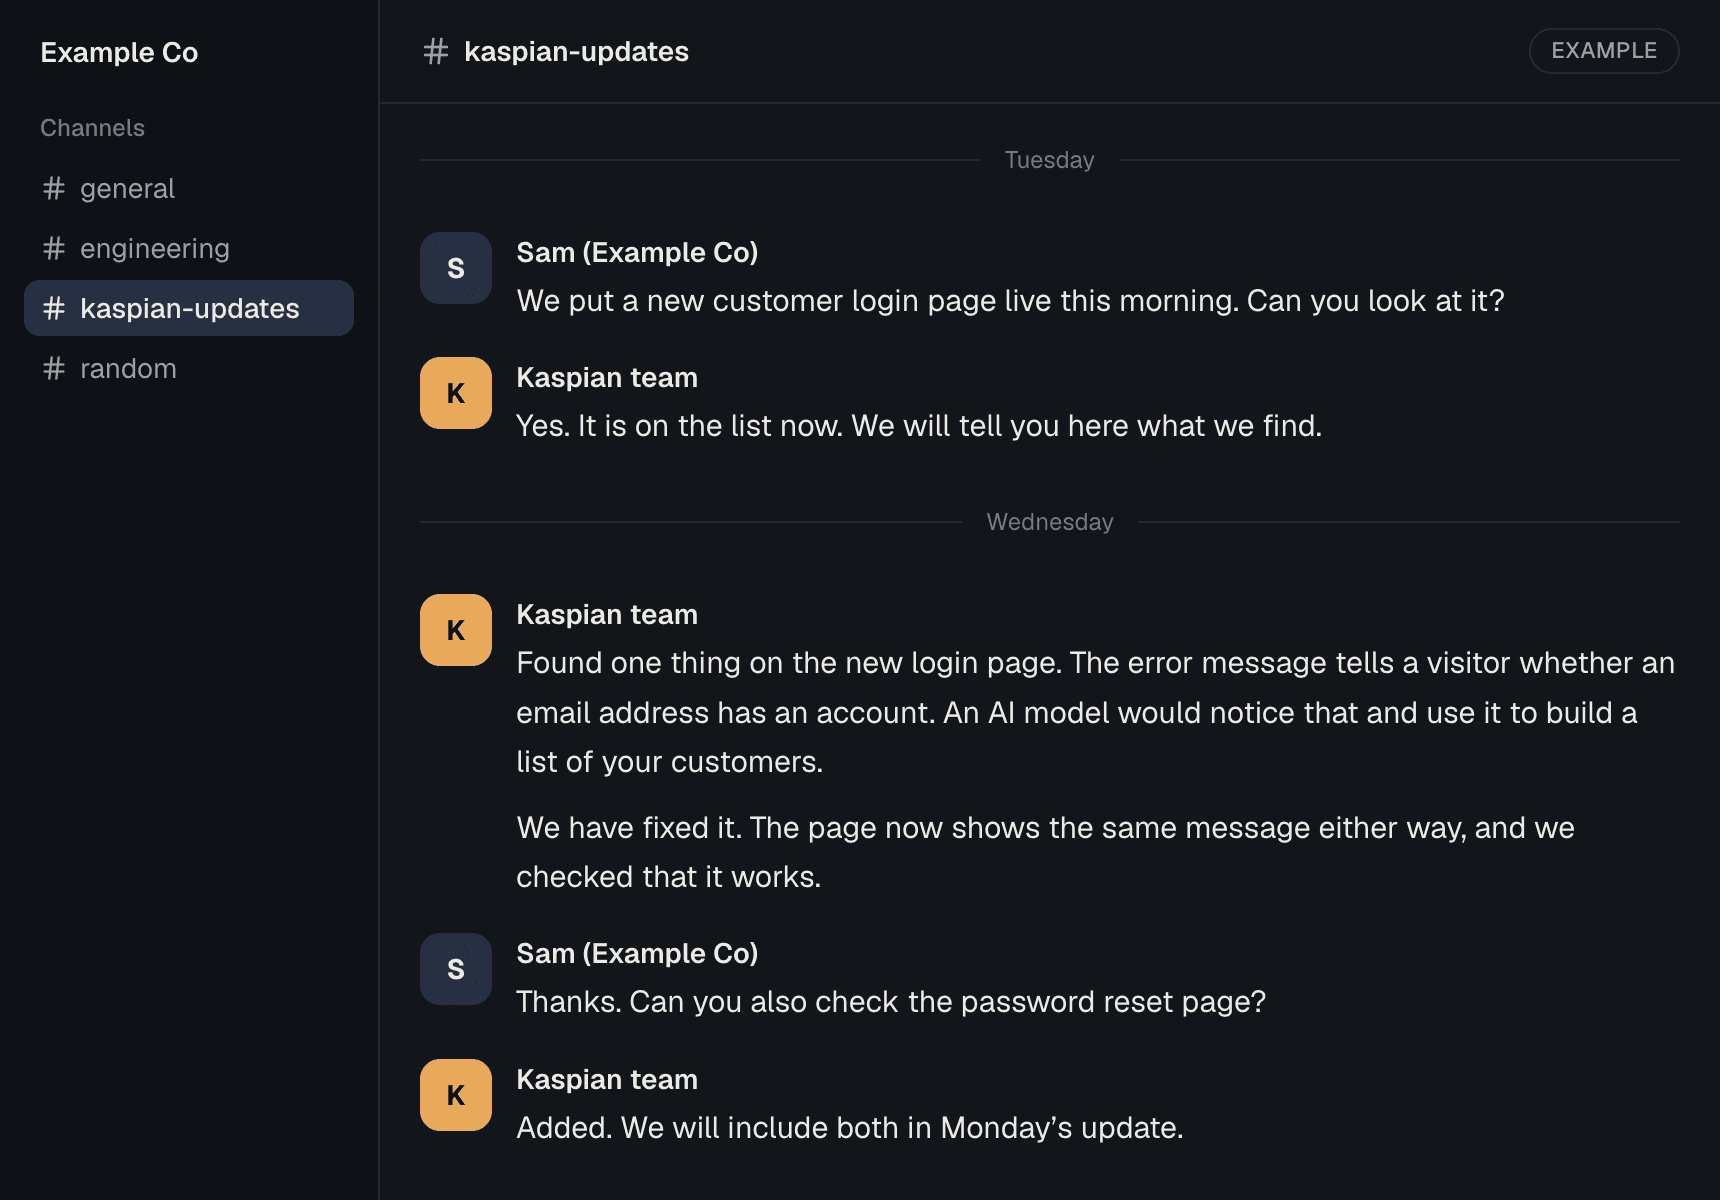
Our team is in your Slack channel all the time. Every week we post a list of what we found, what we fixed and what still needs attention. You can review it all in your dashboard too.
Human customer support 24/7
Our team is in a channel you already use, all the time, not only when an update is due. Ask us a question whenever you have one. Your dashboard has everything we found and fixed, so you can review it whenever you like.
How we compare
| Kaspian | Horizon3.ai | Pentera | XBOW | Cobalt | |
|---|---|---|---|---|---|
| Offers continuous testing | Yes | Yes | Yes | Yes | Yes |
| Checks that a fix worked | Yes | Yes | Yes | Yes | Yes |
| Does the fixing for you | Yes | No | No | No | No |
| Human customer support 24/7 | Yes | No | No | No | No |
Based on each company’s own website, November 2026.
Talk to us about your systems
Tell us what you run and we will explain how Kaspian would work for you.